PeakCyber Technologies

Supply Chain Attack: Trivy, KICS & LiteLLM

Supply Chain Attack: Trivy, KICS & LiteLLM

The Predator Didn’t Wait: How TeamPCP Poisoned the Supply Chain

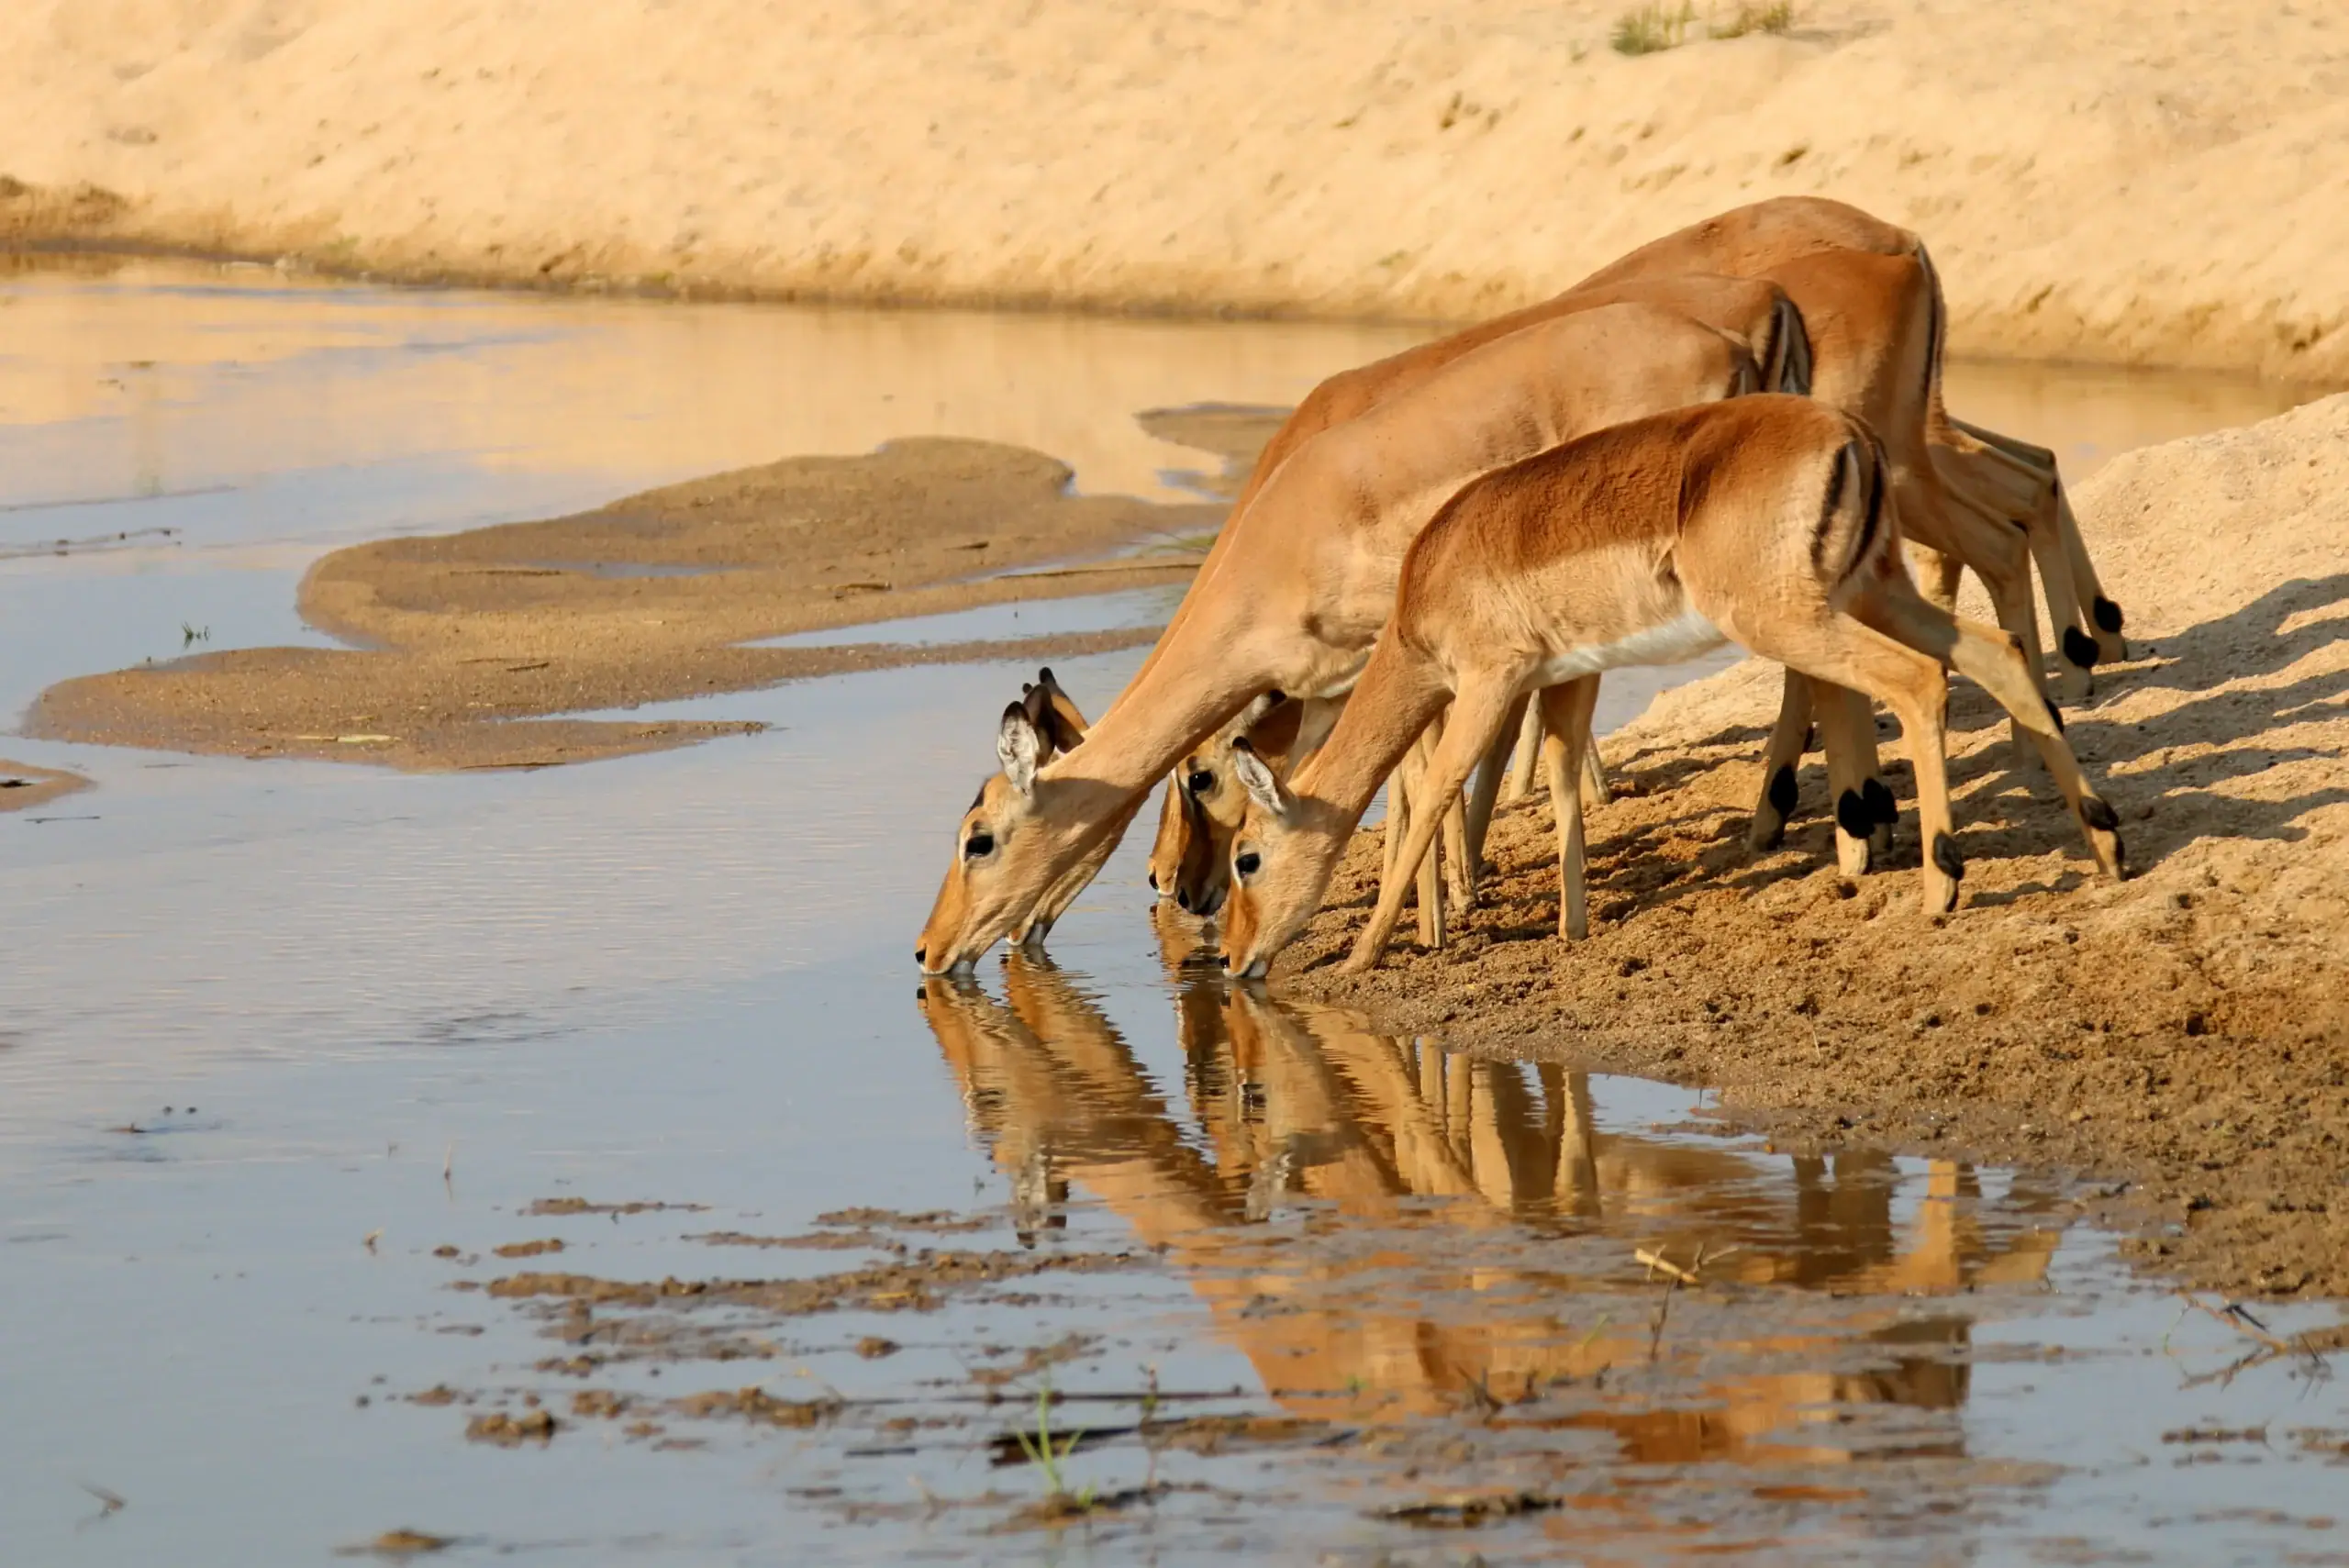
Many of us have seen in documentaries how predatory animals set traps at watering holes and use these traps to hunt other animals that come to drink water. In the world of cybersecurity, there is a technique inspired by this very approach: the Watering Hole Attack.

In the Watering Hole Attack approach, the attacker identifies the systems, infrastructures, and tools that the users of the targeted organization or institution access. The attacker then compromises or leverages these identified systems in order to ultimately reach the users of the organization or institution that is their primary target.

Another attack method in which multiple institutions and users are affected by a single attack is Software Supply Chain attacks. Through malicious code that attackers embed into widely used open or closed source libraries, they are able to carry out numerous actions on target systems — such as establishing remote connections and stealing information, among many others.

So what can happen when these two attacks are combined? The months of February and March 2026 provided many examples to help us understand the answer to this question.

February

Towards the end of February, an AI bot account named HackerBot-Claw demonstrated that sensitive data such as GITHUB_TOKEN and similar credentials could be compromised through misconfigured GitHub Actions workflows in various organizations. In this context, it was found that PAT — Personal Access Token values belonging to organizations such as Microsoft, Datadog, and Aqua Security — Trivy could be obtained.

March

By March 19th, it was detected that a malicious update had been published across the GitHub, DockerHub, and ECR channels belonging to Aqua Security — Trivy. This malicious update was designed to collect sensitive data, passwords, SSH keys, cryptocurrency wallets, and similar information from the system it was running on, then encrypt this data and transmit it to a target C2 server — GHSA-69fq-xp46–6×23

On March 23rd, the target was once again a cybersecurity product: Checkmarx — KICS. The attackers targeted sensitive information using malicious content that operated in exactly the same manner as the Trivy case — KICS Issue 152

All of these attacks were carried out by a threat actor known as TeamPCP. The actor is known to have focused efforts on cloud-native infrastructures.

On March 24th, the victim this time was LiteLLM. An entirely identical attack scenario to Trivy and Checkmarx — collecting all sensitive information from the environment it is running in, encrypting it, and sending it to a C2 server — LiteLLM Issue 24512

A classic Watering Hole attack is passive in nature, the predator sets the trap and waits. However, the TeamPCP incidents reveal an evolved variant of this approach. Rather than waiting for victims to stumble upon a compromised resource, the attacker chose to embed themselves directly into the supply chain of tools that victims were already guaranteed to use — designing a structure that would leave their targets with no opportunity to escape.


Summary

It is once again evident that potential misconfigurations in centrally positioned technologies can pose a serious security threat to a vast number of individuals and organizations.

These incidents serve as yet another reminder that cyberattacks are not a concept we can escape or keep at a distance. Whether we like it or not, we will encounter cyberattacks and we will get hacked. For this very reason, what truly matters is having the capability and competency to rapidly detect and respond when a hacking incident occurs.


PeakCyber cybersecurity and offensive security services logo.

Subscribe to our cyber security newsletter

Scroll to top