PeakCyber Technologies

Internal vs External Penetration Testing: Differences and When You Need Each

Internal vs external penetration testing perspectives

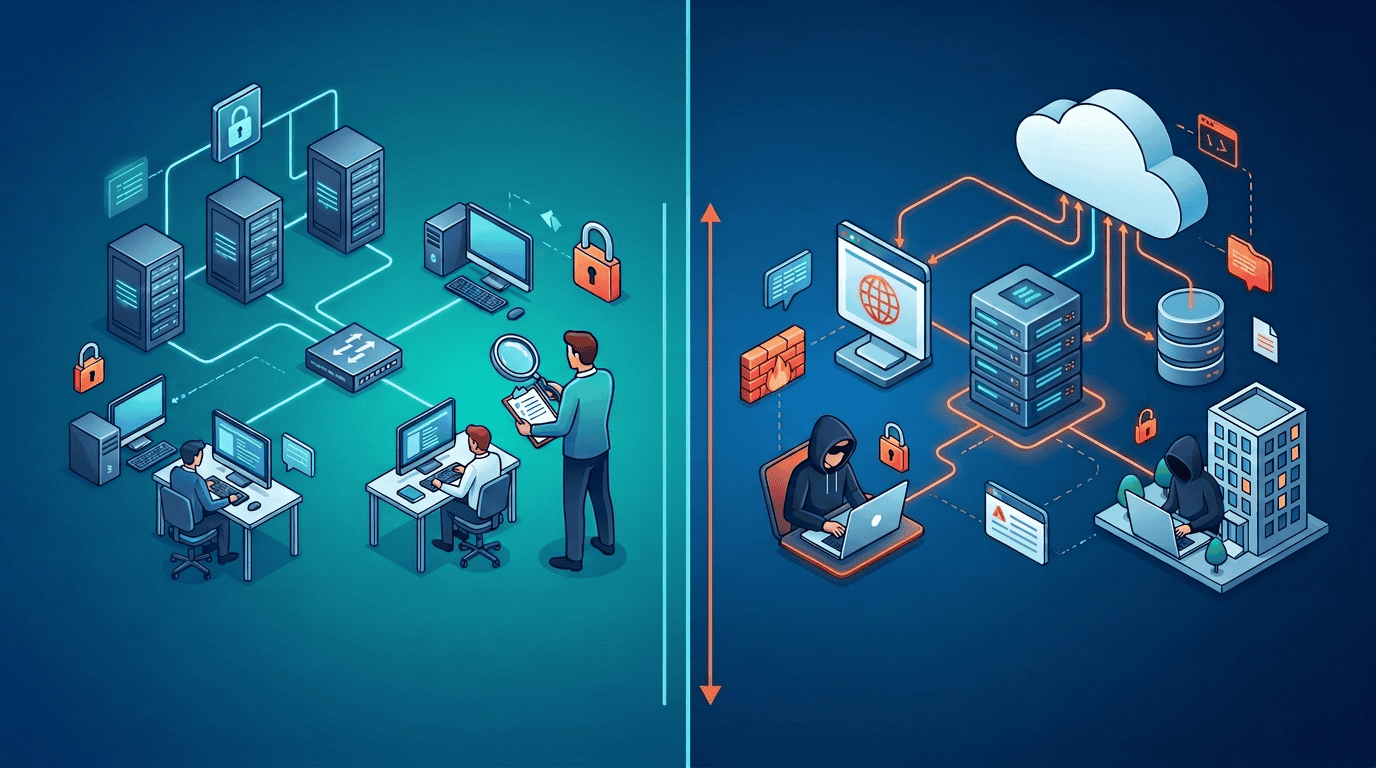
Attackers do not always break in through the front door. Some exploit an exposed service on the internet; others start inside, through a phishing email, a stolen VPN password or a compromised contractor laptop. That is why network penetration testing is usually split into two perspectives: external testing, which looks at your organization from the internet, and internal testing, which starts from inside your network.

This guide explains internal vs external penetration testing: what each one covers, the issues each typically finds, how they differ, what compliance standards require and how to decide which test, or which combination, you need.

What Is External Penetration Testing?

An external penetration test assesses everything an attacker can reach from the internet without any prior access. Testers start from the outside, usually with nothing more than your company name, domains or IP ranges, and try to find a way in.

We initially decided to use Split Query for all our heavy queries. But after a while, we noticed response times were growing significantly on our paginated endpoints — lists returning between 10 and 100 records. Why? Because joining 15 different tables for 10 records (Single Query) is blazing fast, whereas firing 16 separate queries for those same 10 records (Split Query) was causing slowness due to network round-trip latency.

What External Testing Covers

  • Internet-facing infrastructure: public IP ranges, firewalls, routers and load balancers
  • Remote access: VPN gateways, remote desktop services and virtual desktop portals
  • Email and DNS: mail servers, email security configuration and DNS records
  • Web servers and exposed applications: login portals, file transfer services and management interfaces accidentally exposed to the internet
  • Cloud-hosted assets: services and storage reachable from the internet
  • Attack surface discovery: forgotten subdomains, test environments and legacy systems that nobody realized were still online

Common External Findings

  • Remote access services without multi-factor authentication, vulnerable to password spraying or credential stuffing with leaked passwords
  • Unpatched internet-facing devices such as VPN appliances and firewalls, a frequent entry point in real-world attacks
  • Administrative interfaces, databases or development tools exposed to the internet
  • Forgotten or unmanaged assets, such as old staging servers, running outdated software
  • Misconfigured email security that makes spoofing your domain easier

An external test answers one question: can an outsider get in? See our External Penetration Testing service for details.

What Is Internal Penetration Testing?

An internal penetration test starts from a position inside your network, typically the access a regular employee or a compromised workstation would have. The question it answers is different: if an attacker gets in, how far can they go?

This approach is often called assumed breach. It accepts a hard truth: perimeter defenses eventually fail, whether through phishing, a stolen password or a vulnerable device. What matters then is whether an attacker can turn one compromised machine into control of the whole environment.

What Internal Testing Covers

  • Active Directory: misconfigurations, weak or reused passwords, excessive privileges and paths to domain administrator
  • Internal services: file shares, databases, internal web applications and management interfaces
  • Credential exposure: passwords in scripts and shared folders, cached credentials and weak authentication protocols
  • Lateral movement: how easily an attacker can move from one system to another
  • Network segmentation: whether sensitive networks, such as payment or production environments, are really isolated
  • Detection: whether your security monitoring notices the attack as it happens

Common Internal Findings

  • Legacy name resolution protocols (such as LLMNR and NBT-NS) that let attackers capture password hashes on the local network
  • Weak service account passwords that can be cracked offline after requesting Kerberos service tickets (Kerberoasting)
  • Misconfigured Active Directory Certificate Services allowing privilege escalation
  • Local administrator passwords reused across many machines
  • Sensitive data and credentials stored in widely accessible file shares
  • Flat networks where a workstation can reach servers and databases it never needs to reach

In many internal tests, a combination of these issues leads from a standard user account to full domain administrator rights. See our Internal Network Penetration Testing service for details.

Internal vs External Penetration Testing: Key Differences


External penetration testing

Internal penetration testing

Starting point

The internet, with no access

Inside the network, with user-level or network-level access

Simulates

An outside attacker

A compromised employee device, malicious insider or attacker after initial access

Main question

Can an attacker get in?

How far can an attacker go once inside?

Typical targets

Public IPs, VPN, email, exposed services, internet-facing applications

Active Directory, internal servers, file shares, databases, segmentation

Typical findings

Exposed services, missing MFA, unpatched edge devices, forgotten assets

Weak credentials, AD misconfigurations, lateral movement paths, flat networks

How it is performed

Remotely, from the provider’s systems

On site, through VPN or via a device or virtual machine placed in your network

Defenses tested

Perimeter controls and exposure management

Internal hardening, identity security, segmentation and detection

How Internal and External Weaknesses Combine

The two perspectives are most revealing together, because real attacks rarely stop at the perimeter. A typical attack path, of the kind both tests are designed to uncover, looks like this:

  1. External: Testers find a VPN portal without multi-factor authentication. Using a common password pattern against a list of employee names gathered from public sources, they obtain valid credentials for one account.
  2. Initial access: With VPN access, they reach the internal network as a regular user.
  3. Internal: They request service tickets for accounts with service principal names and crack a weak service account password offline.
  4. Privilege escalation: The service account has administrator rights on several servers, one of which has a domain administrator logged in.
  5. Impact: Within hours, testers control Active Directory and can reach any system in the organization.

An external test alone would report “VPN without MFA”. An internal test alone would report “weak service account password”. Together they show the full path from the internet to complete compromise, and that adding MFA to the VPN and fixing service account hygiene each break the chain.

Which One Do You Need?

For most organizations the answer is both, but priorities differ.

Start with external testing if:

  • You have never tested your perimeter, or your internet-facing footprint has recently changed
  • You run remote access, customer portals or other services exposed to the internet
  • You need to demonstrate perimeter security to customers or insurers

Prioritize internal testing if:

  • You rely on Active Directory and have many users and servers
  • You want to understand the impact of a successful phishing attack or ransomware infection
  • You have segmented sensitive environments and need to prove the segmentation works
  • You want to test whether your security monitoring detects an attacker moving inside the network

If your business runs mostly in the cloud with few on-premises systems, the traditional internal network may matter less than identity and cloud configuration. In that case, combine external testing with cloud penetration testing rather than a classic internal test.

What Compliance Standards Require

PCI DSS v4.0.1 is the most explicit standard. Requirement 11.4 calls for both perspectives:

  • 11.4.2: internal penetration testing at least once every 12 months and after any significant infrastructure or application change
  • 11.4.3: external penetration testing on the same schedule
  • 11.4.4: exploitable vulnerabilities found during testing must be corrected and the test repeated to verify the fixes
  • 11.4.5: if segmentation is used to isolate the cardholder data environment, segmentation controls must be tested at least once every 12 months and after changes
  • 11.4.6: service providers must test segmentation at least once every six months

PCI DSS defines internal testing as testing both from inside the cardholder data environment and into it from trusted and untrusted internal networks.

Other frameworks, such as ISO/IEC 27001 and SOC 2, do not prescribe internal and external tests in the same way, but auditors commonly expect regular testing that covers both the perimeter and the internal environment. See our PCI DSS Penetration Testing service for compliance-focused testing.

How Internal Penetration Tests Are Delivered

Internal testing needs a foothold in your network. The common options are:

  • On-site testing: testers connect a laptop to your network at your premises.
  • VPN access: testers connect remotely through an account provisioned for the test.
  • Testing device or virtual machine: a small device or virtual machine is placed in your network and connects back securely to the testers, which avoids travel and works well for multiple sites.
  • Assumed-breach workstation: testers receive a standard employee laptop or virtual desktop with a regular user account, which most closely simulates a phishing victim.

The right option depends on what you want to simulate. Testing from a standard user workstation is the most realistic test of what happens after a successful phishing attack.

How to Prepare

For an external test:

  • List all domains, subdomains and public IP ranges you own, including those hosted by cloud and SaaS providers
  • Confirm you have permission to test assets hosted by third parties, and check each provider’s testing policy
  • Tell your security monitoring team and hosting provider about the test window and the testers’ source IP addresses

For an internal test:

  • Decide what to simulate: a standard user, a contractor or an attacker with only network access
  • Prepare the access method: VPN account, testing device or workstation
  • Identify critical systems that need extra care and agree on any techniques that are off limits
  • Decide whether your security team should know about the test, or whether detection is part of what you are testing

For both, agree on emergency contacts and how critical findings will be reported during the test. Our guide to what to expect in a penetration test report explains what you should receive at the end.

Frequently asked questions

1
Is an internal penetration test necessary if our perimeter is secure?
Yes. Phishing, stolen credentials and vulnerable edge devices mean that every organization should assume an attacker may eventually get inside. An internal test shows whether that would be a contained incident or a full compromise.
2
How long do internal and external tests take?
An external test of a small to medium perimeter typically takes several days to a week; an internal test of a single site with Active Directory typically takes one to two weeks. Larger or multi-site environments take longer.
3
Will internal testing disrupt our network?
Testers avoid disruptive techniques unless explicitly agreed, and risky actions are coordinated in advance. Rules of engagement define testing windows and any systems that need special care.
4
Can internal testing be done remotely?
Yes. A VPN connection, a testing device or a virtual machine placed in your network allows internal testing without testers being on site.
5
How is this different from a red team exercise?
Internal and external penetration tests aim to find as many exploitable weaknesses as possible within a defined scope. A red team exercise simulates a specific adversary trying to reach an objective while avoiding detection, testing your detection and response as much as your vulnerabilities. Read more in What Is Penetration Testing?

Conclusion

External penetration testing tells you whether an attacker can get in. Internal penetration testing tells you what happens when they do. Because real attacks combine both, the clearest picture of your risk comes from testing both perspectives and looking at how weaknesses connect from the internet all the way to your most critical systems.

Want to see your network from an attacker’s perspective? Explore our External and Internal Network Penetration Testing services, or talk to our team to plan an engagement. To build these skills in-house, see our Network Penetration Testing Training.


PeakCyber cybersecurity and offensive security services logo.

Subscribe to our cyber security newsletter

Scroll to top